How Replit Solved the “Runaway Token Budget” Problem in Agent Workforces
AI agents can now do real business work. They research markets, build software, test products, prepare sales materials, and keep iterating toward a goal. That capability brings a worry that every CFO, CIO, and platform lead recognizes: what happens when an agent just keeps working, keeps calling models, keeps using tools, and keeps spending? Replit’s … Read more
The Compute Black Market: How Underground “LLM Mixers” Fuel Autonomous Attack Pipelines

The next underground economy might not revolve around stolen databases, malware kits, or ransomware access. It might revolve around something quieter: the ability to run commercial AI models on someone else’s dime. Security researchers call this LLMjacking: stealing or misusing AI credentials, API keys, and access tokens to burn through a victim’s AI resources. The … Read more

Why Uber’s Execution Tracing and Event Replay Are Essential for Multi-Agent Reliability

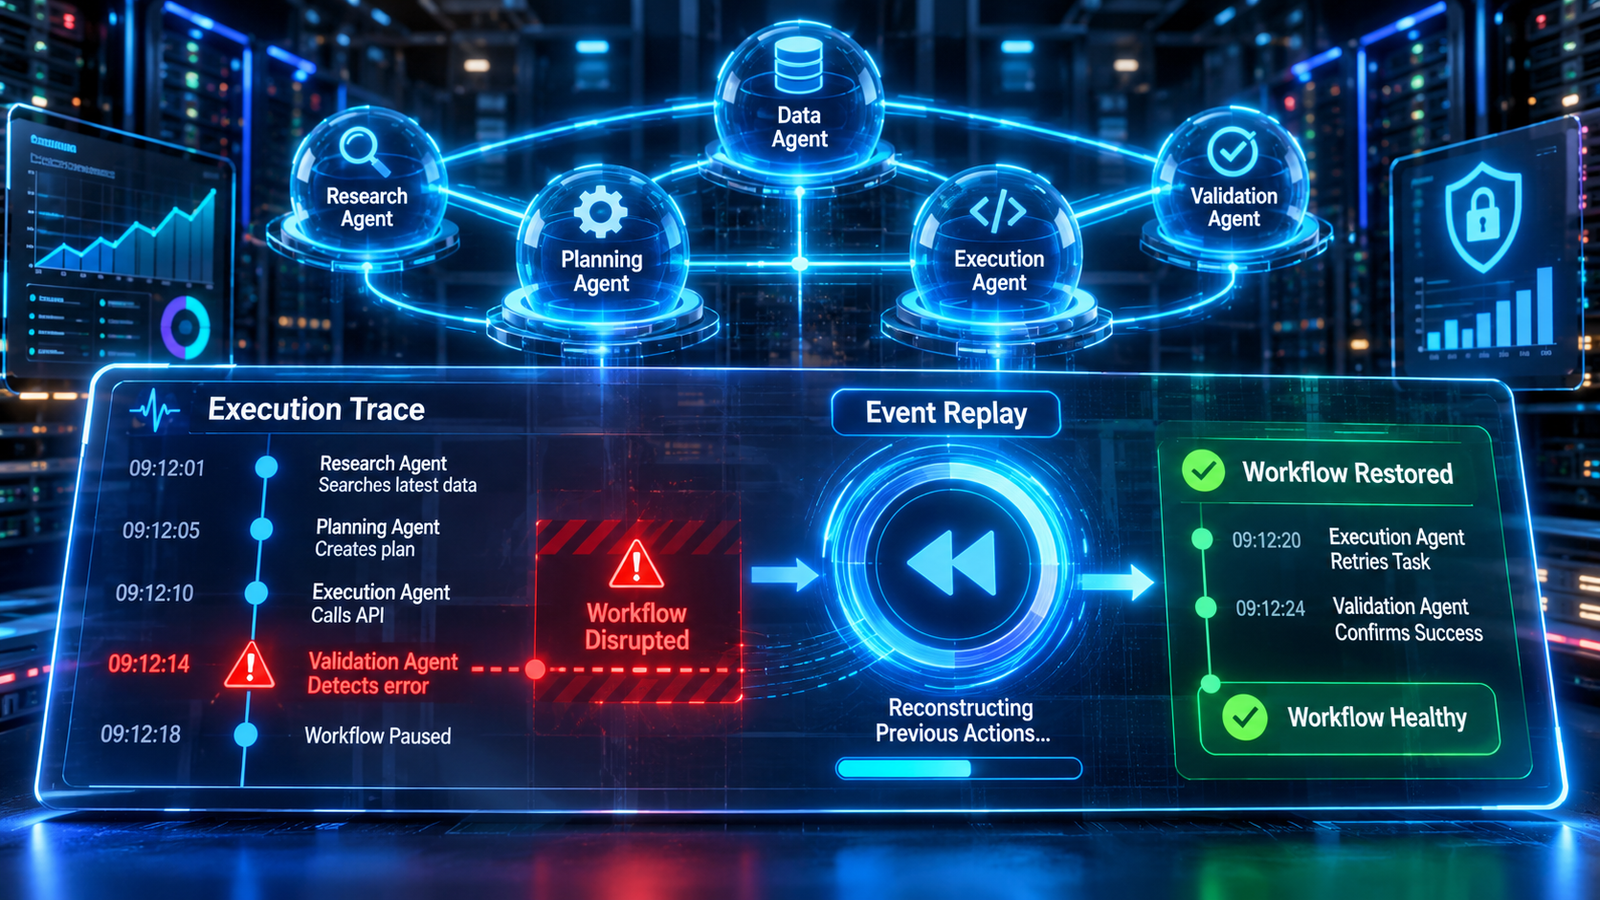
Traditional software testing asks a simple question: does the code behave as expected under conditions we already know about? Agentic AI breaks that assumption. An agent can interpret ambiguous input, pick its tools on the fly, act across several systems, and produce different results depending on what has happened in the session. Static tests and … Read more

Why Open-Source Orchestration, Not Model Intelligence, Is the Real Cyber Threat Vector

The biggest shift in offensive AI isn’t that language models got dramatically smarter. It’s that open-source agent harnesses now let ordinary LLMs work like persistent, tool-using, multi-stage systems. They plan, act, check the result, adjust, and keep going with very little human supervision. Most of the security debate has fixated on whether a frontier model … Read more

The Sovereign Multi-Agent Performance Playbook: How to Reduce Latency, Prevent Error Compounding, and Maximize Throughput

Running AI agents inside your own walls gives you control, privacy, and independence. It also hands you a problem nobody warns you about: you now own the compute, the queues, the failures, and the cost of every unnecessary agent turn. The teams that get this right don’t just add more agents or buy faster GPUs. … Read more

The Forensic Footprints of “Noisy” Autonomous AI Attack Swarms

For years, “AI hacking” has been treated as one big threat. A model writes some malware, a chatbot drafts a phishing email, and defenders are told to brace themselves. That framing misses the bigger shift happening right now. Autonomous AI agents are changing the economics of intrusion. Vulnerability research, exploit development, targeting and execution can … Read more