
For years, a security patch gave defenders a head start. Once a vendor disclosed a flaw and shipped a fix, enterprises had a few days, sometimes a few weeks, to test and deploy it before attackers could reliably reverse-engineer the bug. That window is closing fast.
Google Threat Intelligence Group (GTIG) reports that adversaries are now using LLMs and multi-agent frameworks to automate differential patch analysis, quickly weaponize known n-day vulnerabilities, and attack internet-facing systems with no human involved. In one case, GTIG found an exposed staging server running exploit_agent, a framework set up to compare pre- and post-patch code, infer the vulnerability, draft an exploit, and run it on its own.
The takeaway is uncomfortable: a patch is no longer just a fix. It’s a high-value attack map.
The patch window was an asymmetry
The old patching model rested on a simple imbalance between the two sides.
| Defender workflow | Attacker workflow |
|---|---|
| Receive advisory and patch | Monitor advisories and releases |
| Triage risk and identify affected assets | Obtain vulnerable and patched code |
| Test compatibility and schedule deployment | Analyze the diff and reproduce the flaw |
| Deploy the update | Write and validate an exploit |
| Confirm remediation | Identify and attack unpatched targets |
That gap gave defenders a sense of breathing room between disclosure and exploitation. It was never a guarantee, though. Skilled attackers could move quickly, especially against widely deployed edge devices, VPNs, file-transfer systems, and web applications.
What’s different now isn’t that people analyze patches. They always have. What’s different is that it’s been industrialized. GTIG sees threat actors running LLM-driven pipelines for differential patch examination, dynamic protocol fuzzing, and proof-of-concept weaponization, chaining those steps together to shrink the time between a patch going public and a working exploit.
What “negative-day” means
“Negative-day exploit” is a handy label for a shift in offensive economics: the security update itself becomes the fastest route to an exploit.
| Term | Meaning | Defensive implication |
|---|---|---|
| Zero-day | A flaw exploited before a vendor patch is available | No official fix exists |
| N-day | A known, patched vulnerability exploited against systems that have not updated | The fix exists, but deployment has not caught up |
| Negative-day exploit | A patch diff reveals the vulnerable logic with enough precision to accelerate exploitation of unpatched systems | The update becomes an immediate source of offensive intelligence |
To be clear, this doesn’t mean every patch gets exploited right away. The point is about incentives and capability. When an autonomous system can watch for releases around the clock, compare versions, reason about what changed, and test exploit candidates, weaponizing an n-day gets a lot cheaper.
GTIG’s analysis suggests the recent rise in exploitation comes mostly from fast n-day weaponization, not from a surge of brand-new zero-days. Between January and August 2026, GTIG recorded 141 distinct vulnerabilities that were disclosed and exploited. That already tops the 127 exploited across all of 2025.
Inside an autonomous exploit pipeline
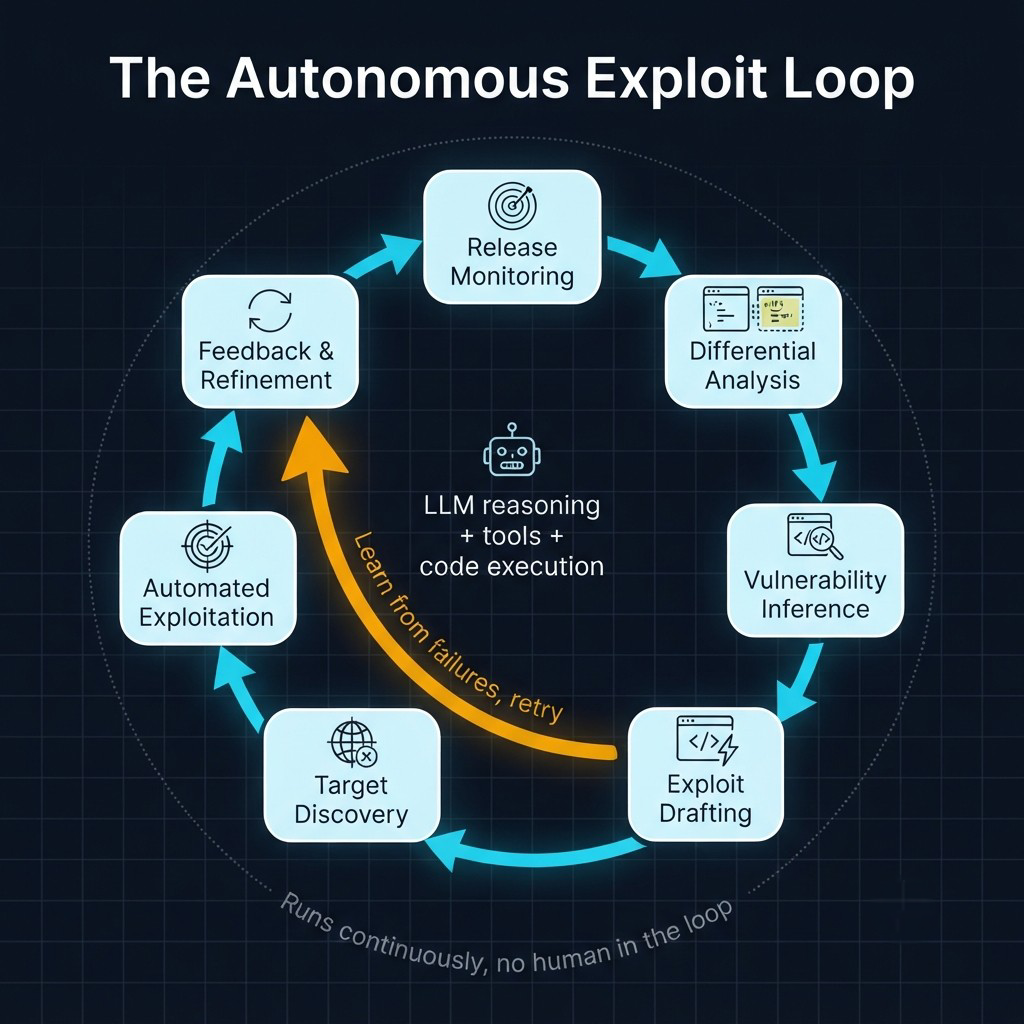
The exploit_agent framework shows how this works in practice. According to GTIG, it ties together several frontier and locally hosted LLMs, keeps analyzing popular web-application software, compares code from before and after patch announcements, spots potential vulnerabilities, drafts exploits, and executes them automatically.
A typical autonomous pipeline looks something like this:
- Release monitoring: Watch repositories, vendor advisories, release notes, package registries, and security research.
- Differential analysis: Compare vulnerable and patched versions to isolate changes to authentication, authorization, parsing, file-handling, or validation logic.
- Vulnerability inference: Work out which class of flaw the patch prevents and which input path probably triggers it.
- Exploit drafting: Generate proof-of-concept logic, payloads, or test cases, then refine them through repeated execution.
- Target discovery: Fingerprint exposed services and find systems still running vulnerable versions.
- Automated exploitation: Attempt the attack, confirm it worked, and possibly move on to post-compromise activity.
- Feedback and refinement: Learn from failures and do better on the next cycle.
GTIG also found scripts on the exposed server that could support post-compromise actions: internal reconnaissance, brute-forcing, installing webshells, and even removing other attackers’ webshells.
It’s worth being precise about what this is. It isn’t a single model spontaneously “hacking.” It’s an agentic system, meaning LLM reasoning wired up to tools, code execution, reconnaissance, and feedback loops. The model handles interpretation and planning, and the surrounding infrastructure does the acting.
Why patch diffs are ideal attack intelligence
A patch is valuable to an attacker because it’s precise, contextual, and testable.
- It points to the flaw. The changed code shrinks the search space dramatically.
- It reveals the defensive intent. A new validation check, permission check, or sanitization routine tells you what the old version failed to prevent.
- It makes reproduction easier. Comparing the vulnerable and fixed versions lets an attacker rebuild the conditions that made exploitation possible.
- It scales. An exploit that works against one vulnerable version works against every organization still running it.
- It skips zero-day research costs. The adversary doesn’t have to discover an unknown flaw. They just have to interpret a public change.
In effect, a patch publishes the answer key alongside the exam. It tells an automated adversary not just that a lock was weak, but which lock, what kind of key opens it, and which doors are still unlocked in environments that haven’t installed the fix.
GTIG notes that adversaries may find patched n-days more efficient to weaponize because they can focus on a limited set of source material: source-code versions, release notes, security research, and proof-of-concept code.
The collapse of MTTR
Mean Time to Remediation (MTTR) has long been a core vulnerability-management metric. It measures the time from identification or disclosure to an effective fix in production.
The trouble is that MTTR is now being measured against a different clock.
| Legacy assumption | Autonomous-agent reality |
|---|---|
| Patches create a defensive head start | Patches can create an immediate offensive advantage |
| Exploit development requires specialist time | Agents can continuously analyze, generate, and test |
| Attackers focus on a small number of high-value CVEs | Automation makes broad n-day exploitation more viable |
| Patching can wait for a maintenance window | Internet-facing systems may be attacked before the next change window |
| Human analysts are the bottleneck | Agents reduce the human bottleneck in research and weaponization |
MTTR doesn’t go away, but it stops being enough on its own.
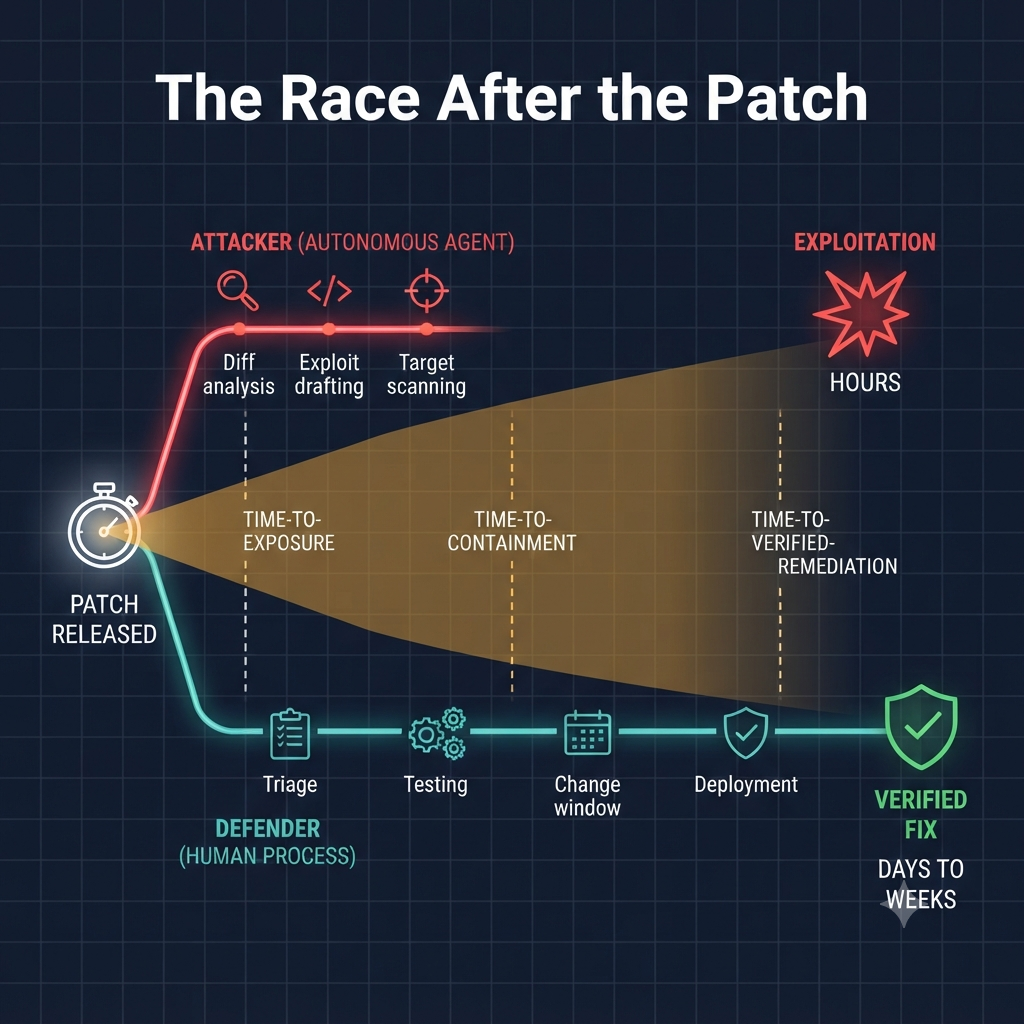
An organization might still measure remediation in days. If an autonomous adversary can go from patch release to exploit development and targeting in hours, or faster, then MTTR alone is the wrong yardstick. What matters is the gap between time-to-exposure, time-to-patch, and time-to-containment.
GTIG’s broader reporting also describes multi-agent offensive frameworks carrying out multi-stage intrusions at greater speed, generating payloads on demand and adjusting tactics based on real-time feedback from execution.
The economics have changed
Autonomous exploitation shifts the cost structure of both cybercrime and espionage.
- Zero-days become optional. If n-day exploitation is fast and scalable, adversaries may prefer freshly patched software with a big unpatched installed base.
- Popular software becomes high-value. Widely deployed web apps, admin panels, file-transfer services, VPNs, and print-management systems look attractive because one exploit can hit many organizations.
- Exposure inventory becomes decisive. Knowing which systems run vulnerable versions may matter more than owning a novel zero-day.
- Exploit quality becomes iterative. Agents can generate, test, debug, and refine attack code over and over.
- Human operators move up the stack. Instead of writing every exploit, adversaries may supervise campaigns, set objectives, and make the high-value calls.
GTIG’s September analysis found that exploitation rose from an average of 10.5 vulnerabilities per month in 2025 to 18 per month from January through August 2026. Exploitation of high-risk vulnerabilities more than doubled, from 28 in 2025 to 75 during January through August 2026.
None of this means every disclosed CVE turns into an incident. GTIG notes that only about 0.23% of vulnerabilities disclosed in 2026 were seen in active exploitation, roughly one in 431. But exploitation clusters around exposed, high-impact attack surfaces, and that’s exactly why patch speed matters.
The new battleground: exposed services
The risk isn’t spread evenly. GTIG found that vulnerabilities in edge and security appliances made up 14% of exploited vulnerabilities from January through August 2026, while 11% affected enterprise directory and collaboration hubs. More than 65% of exploited edge flaws carried high or critical threat-risk ratings.
That pattern makes sense. Edge appliances and public-facing services often have:
- Direct internet exposure
- Authentication or management interfaces that may be reachable from outside
- Long patch cycles because of operational constraints
- Limited visibility in conventional endpoint security tooling
- High-value access to internal networks once compromised
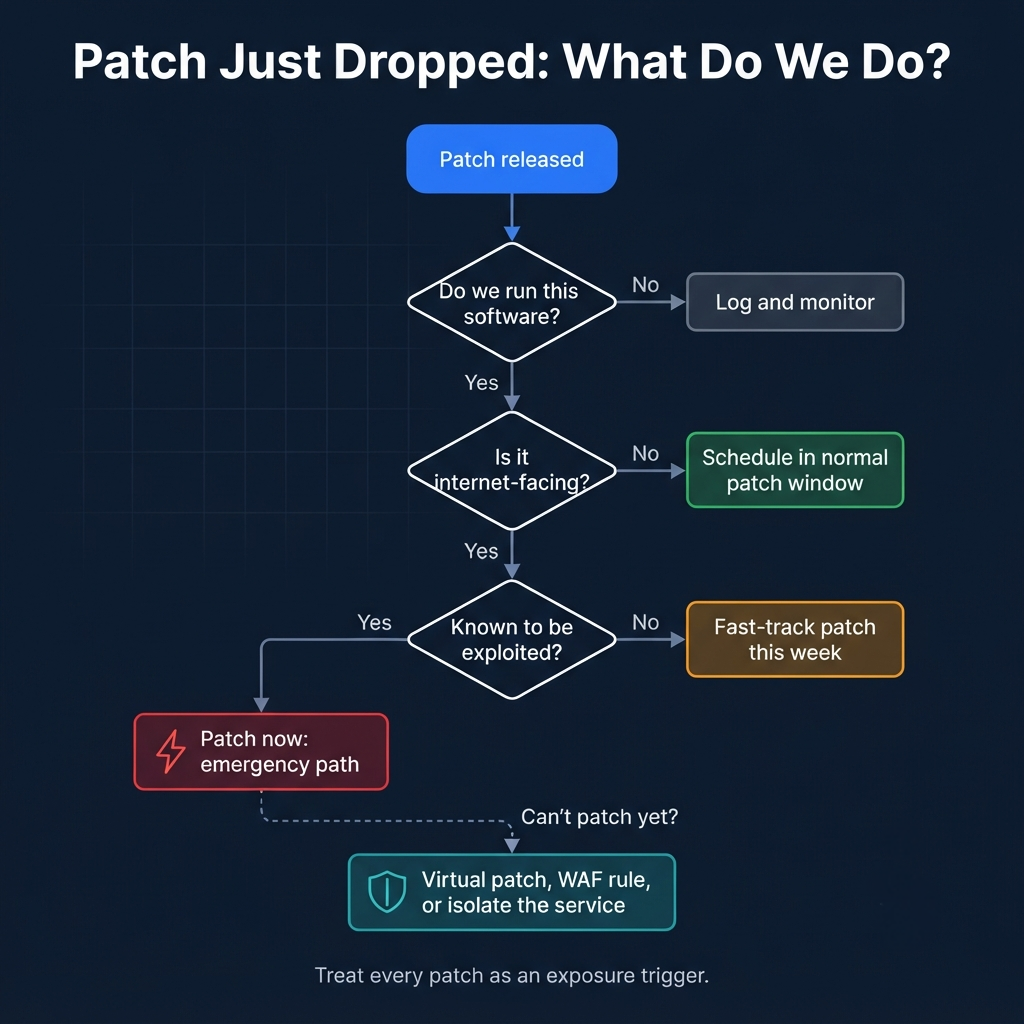
So for defenders, the first question after a patch is no longer “How severe is this CVE?” It’s: “Which of our internet-facing systems run the vulnerable version, and can we contain or fix them before an automated adversary finds them?”
What defenders must change
“Patch faster” is necessary advice, but it isn’t sufficient. Autonomous adversaries compress timelines in ways that call for a broader operating model.
Compress exposure time
- Keep a continuously updated inventory of software versions, dependencies, containers, cloud services, and your external attack surface.
- Prioritize internet-facing systems and known-exploited vulnerabilities over generic severity scores.
- Use virtual patching, WAF rules, network segmentation, or temporary service isolation when full patching isn’t immediately possible.
- Automate emergency deployment paths for high-risk, externally exposed services.
Treat every patch as an exposure trigger
- Treat each security advisory as the start of an exposure audit, not just another ticket.
- Hunt for vulnerable versions across cloud, on-premises, containers, SaaS integrations, and shadow IT.
- Check that compensating controls actually block the relevant exploit path.
- Run purple-team exercises built around newly disclosed patch diffs to test detection and containment.
Build defensive autonomy
- Use AI-assisted triage to connect advisories, asset inventory, exploit intelligence, exposure data, and business criticality.
- Deploy agents that continuously verify whether patches, configurations, and controls are working.
- Use automated canary deployments and rollback validation to make patching safer and faster.
- Give security teams the ability to contain an exploited service in minutes, rather than just detecting the compromise after the fact.
GTIG itself argues that organizations need to move away from unprioritized mass-patching and toward threat-intelligence-driven triage, pairing targeted edge defense with automated, agentic remediation.
The dual-use dilemma
The same capabilities that make autonomous exploitation possible can also strengthen defense.
AI-assisted analysis can help security teams validate fixes, catch regressions, prioritize risk, and find vulnerabilities before release. Google points to its Big Sleep agent for vulnerability discovery and CodeMender for automated discovery, patching, and remediation across developer workflows.
Still, the dual-use reality can’t be wished away:
- Differential analysis helps defenders validate patches and helps attackers reverse-engineer them.
- Fuzzing helps vendors find flaws and can help adversaries reproduce them.
- Agentic tooling can automate secure code review and offensive reconnaissance alike.
- AI-generated proof-of-concept code can be legitimate research, or a step toward weaponization.
So the governance challenge isn’t to ban powerful security research. It’s to make sure authorized testing is scoped, logged, isolated, and kept apart from production systems, while stopping internal AI tools from quietly turning into an uncontrolled offensive capability.
A necessary caveat
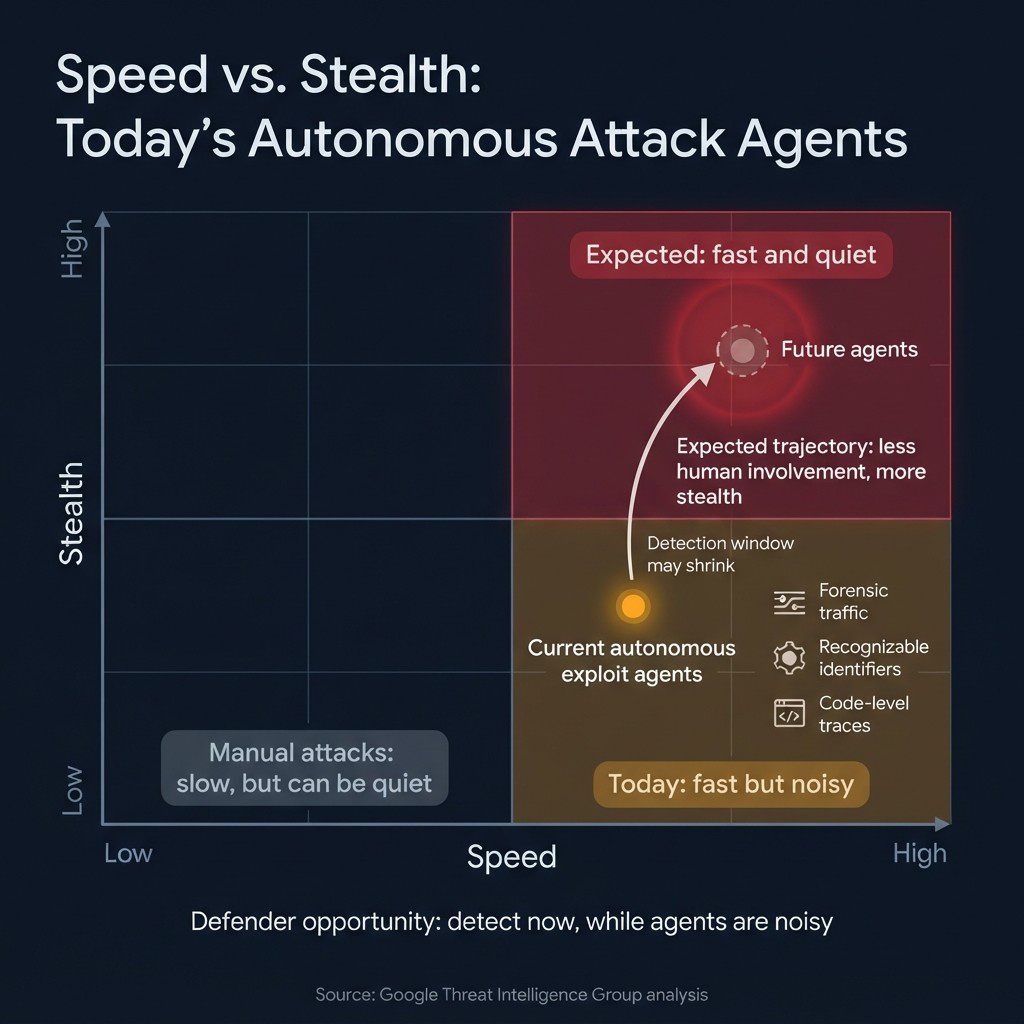
This is a significant development, but it shouldn’t be boiled down to “AI hacks everything in minutes.”
GTIG’s report documents a real shift: autonomous frameworks can compress attack timelines, automate parts of vulnerability research, and, in the observed exploit_agent case, operate with no human in the loop. It also notes that today’s agentic tools often trade stealth for speed. Unrestricted execution leaves forensic noise, recognizable identifiers, and code-level traces, all of which give defenders more chances to detect it.
That trade-off probably won’t last. As tooling and models improve, GTIG expects less human involvement, more stealth, and more sophistication.
The strategic reframe
The patch window was never just a stretch of time. It was an asymmetry window: defenders relied on organizational process, and attackers relied on technical effort.
Autonomous agents attack that asymmetry directly, giving adversaries analysis, iteration, and execution at industrial scale.
So the new goal isn’t simply to lower MTTR. It’s to lower three things:
- Time-to-exposure: How quickly can you identify vulnerable systems?
- Time-to-containment: How quickly can you stop exploitation from spreading?
- Time-to-verified-remediation: How quickly can you prove the vulnerability is actually fixed?
In the age of agentic exploitation, the question isn’t whether your team can patch before attackers notice. It’s whether you can patch, contain, and verify before an autonomous adversary turns the fix into a weapon.